Vulnerability Management helps you to identify and fix vulnerabilities on managed resources. It provides a summary of affected resources, active CVEs, severity levels, available patches, and remediation status.
You can use Vulnerability Management to:
- Identify affected resources.
- Review vulnerabilities by resource or CVE.
- View affected packages and available fixed versions.
- Select vulnerabilities for remediation.
- Review completed remediation instances.
Prerequisite
Before using Vulnerability Management:
- Install the OpsRamp Agent on the resource.
- Run an asset information scan regularly. Create vulnerbility Scan job from Automation >Jobs, it will request for asset info to agent
- Ensure that the resource reports its latest software and package information.
- Ensure that you have permission to access Patch Management and perform remediation.
Note
This is a beta feature available behind a feature flag. Contact the OpsRamp Support team to enable this feature.How vulnerability information is collected
Steps to collect vulnerbilities
- create vulnerbility scan job from Automation by add resources
- For linux: The cloud request for asset info to agent
- For windows: The request for Patch Scan
- OpsRamp uses latest asset/patchScan details to identify vulnerbilities
- Run Vulnerbility Scan daily
Access Vulnerability Management
To open Vulnerability Management:
- Log in to the OpsRamp portal.
- Select a client from the All Clients list.
- Go to Configuration Management > Patch Management.
- Select the hamburger menu icon in the upper-left corner.
- Select Vulnerability Management.
- The Vulnerability Management dashboard page appears.
Vulnerability Management dashboard
The Vulnerability Management dashboard provides a summary of detected vulnerabilities and affected resources for the selected client.
Use the dashboard to understand the overall vulnerability exposure before investigating individual resources or CVEs.
Dashboard widgets
| Widget | Description |
|---|---|
| Affected Resources | Number of resources affected by one or more detected vulnerabilities. |
| Vulnerability Severity Breakdown | Distribution of active vulnerabilities across Critical, High, Medium, and Low severity levels. |
| Affected Resources by Operating System | Operating systems affected by vulnerabilities and the corresponding number of impacted resources. |
| Active CVEs | CVE’s which are active (open/not fixed) on the affected resources. |
| Remediable CVEs | Number of detected CVEs for which a vendor advisory or patch is available. |
| Deployable Patches | The CVEs Which are having patches available against the resources to fix the CVEs. |
| Known Exploited Vulnerabilities (KEV) | A KEV confirmed as actively targeted or exploited in real-world attacks. |
Note
An active CVE might not be remediable if a vendor fix or applicable patch is unavailable.Once you click on any of the number from the dashboard, it will be landed to the Vulnerability Inventory page. Example, here i am clicking on impacted resources number (2).
Vulnerability Inventory
The Vulnerability Inventory displays detailed vulnerability information through the following tabs:
- Resources
- CVEs
Use the Resources tab to investigate vulnerabilities affecting individual resources. Use the CVEs tab to investigate a specific vulnerability across affected resources.
View Vulnerability Details by resources
The Resources tab lists resources affected by detected vulnerabilities.
To view affected resources:
- Go to Vulnerability Inventory.
- Select the Resources tab.
Resource severity summary
The counters at the top of the Resources tab summarize affected resources by severity:
- All
- Critical
- High
- Medium
- Low
Select a counter to filter the resource list by the corresponding severity.
Resource details
View the CVE Insights Page
Follow the steps below to see the CVE Insights page:
- Login to OpsRamp Portal.
- Select a client from the All Clients list.
- Go to Configuration Management > Patch Management.
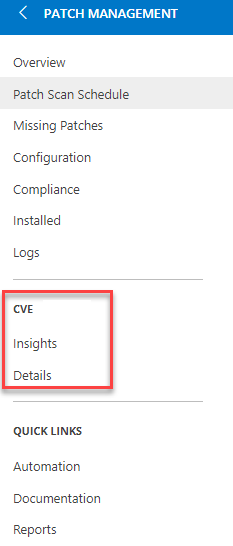
- On the left side of this page, click the Menu bar icon.
- Click the Insights under the CVE tab.
- Here you will see CVE Insights landing page.
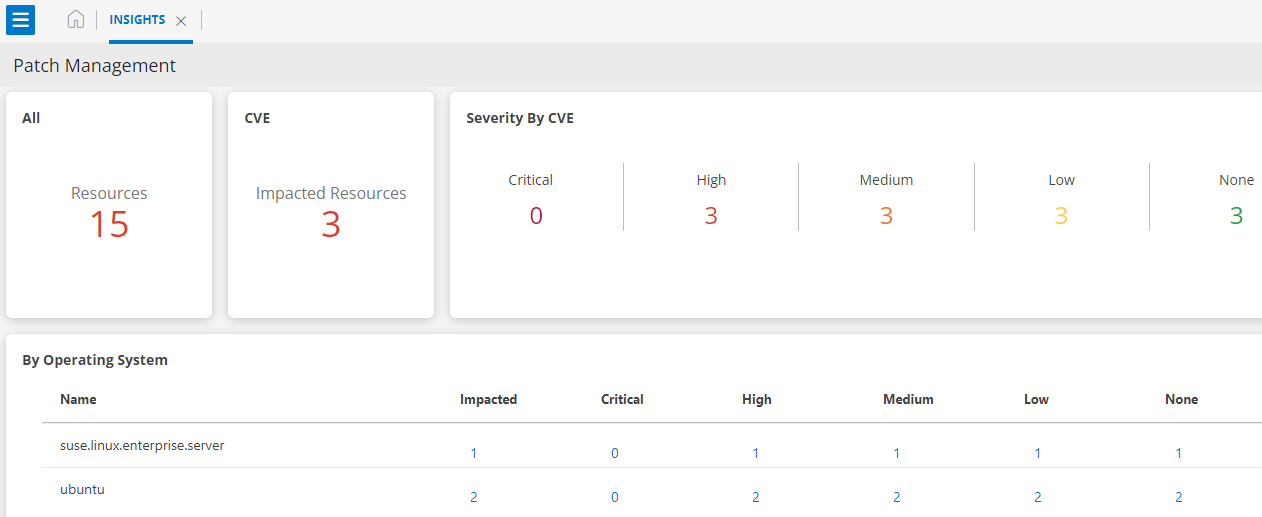
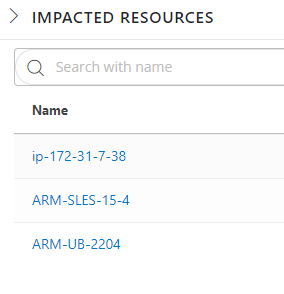
By clicking on any of the displayed numbers above, it will provide you with detailed information. Here is an example of what you can expect when click on “Impacted Resources”:
The following table describes the various widgets displayed on the Insights page:
| Widgets | Description |
|---|---|
| Resources | See the total number of resources for the selected client. |
| Impacted Resources | Number of resources impacted for CVE out of of total resources. |
| Severity By CVE | Type of Severity impacted for each resources: - Critical - High - Medium - Low - None |
| By Operating System | See the list of operating system impacted by CVE with Severity categories. |
View the CVE Details Page
Follow the steps below to see the CVE Details page:
- Login to OpsRamp Portal.
- Select a client from the All Clients list.
- Go to Configuration Management > Patch Management.
- On the left side of this page, click the Menu bar icon.
- Click the Details under the CVE tab.
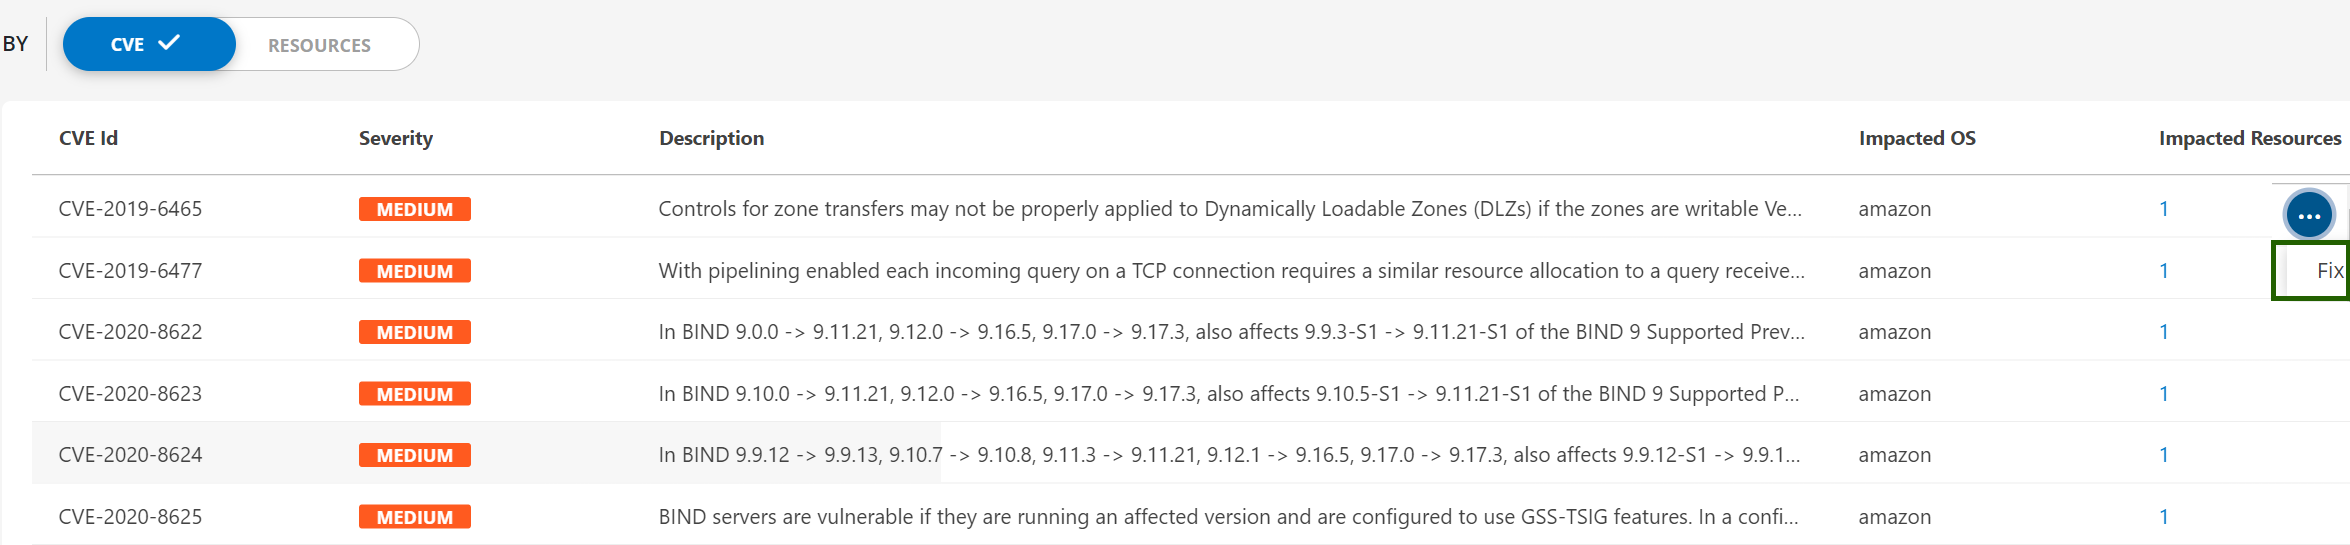
- Here you will see CVE Details listing page. You can view the CVE details by selecting the CVE or RESOURCES option.
By using CVE option:
The CVE option enables you to view the list of CVE id for the impacted devices.
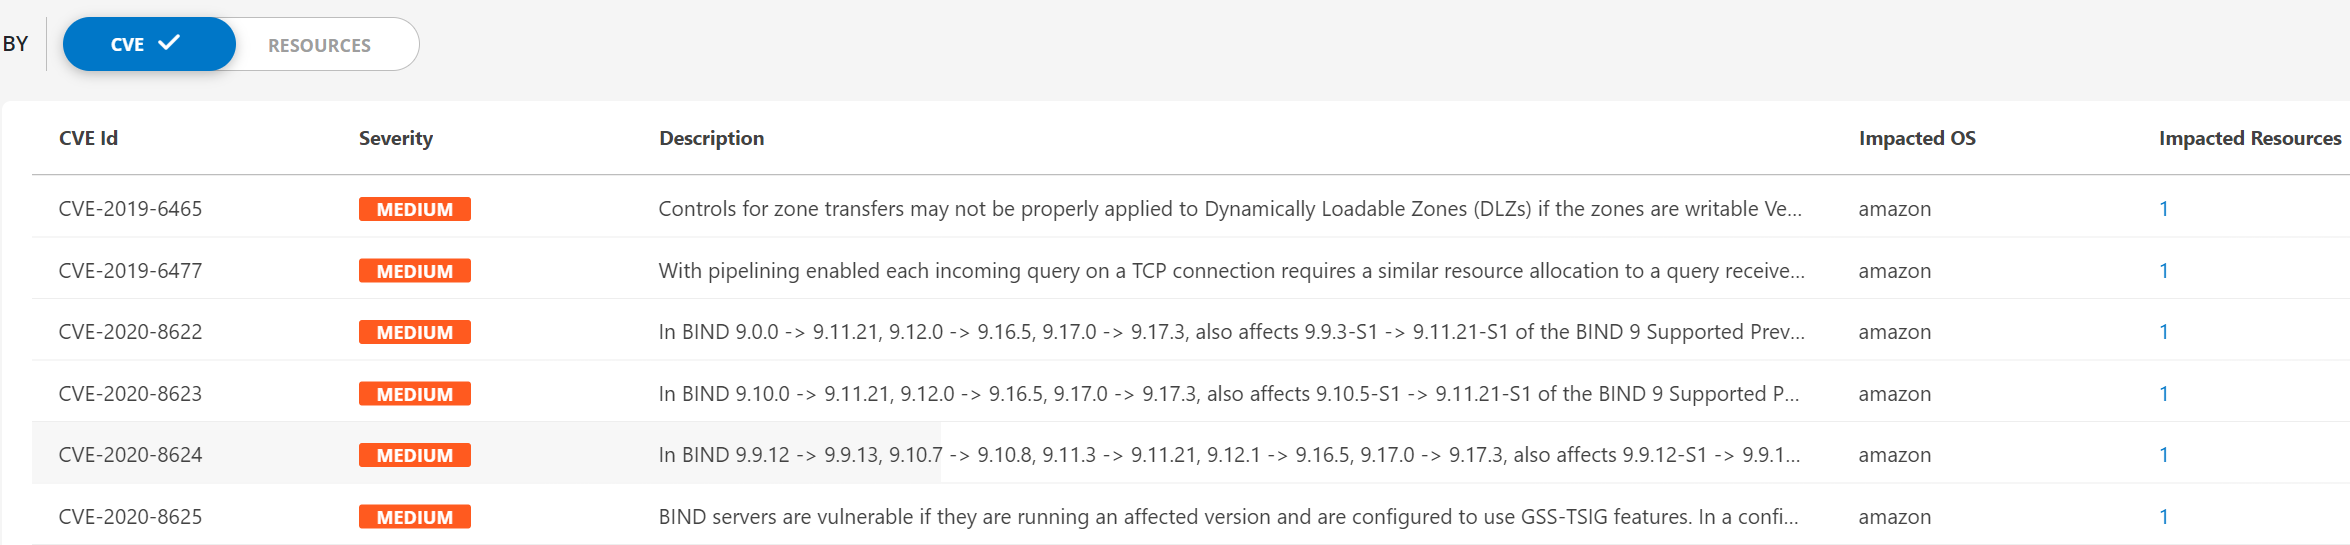
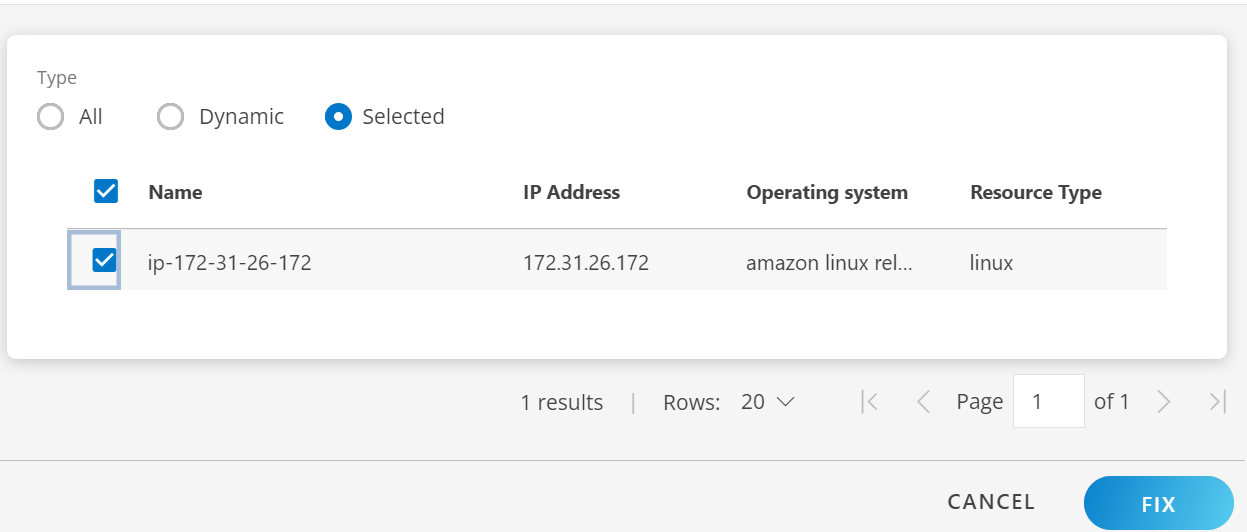
You can fix the CVE for impcted resources by clicking Fix option.
By using RESOURCES option:
The RESOURCES option enables you to view the list of devices with the number of CVE.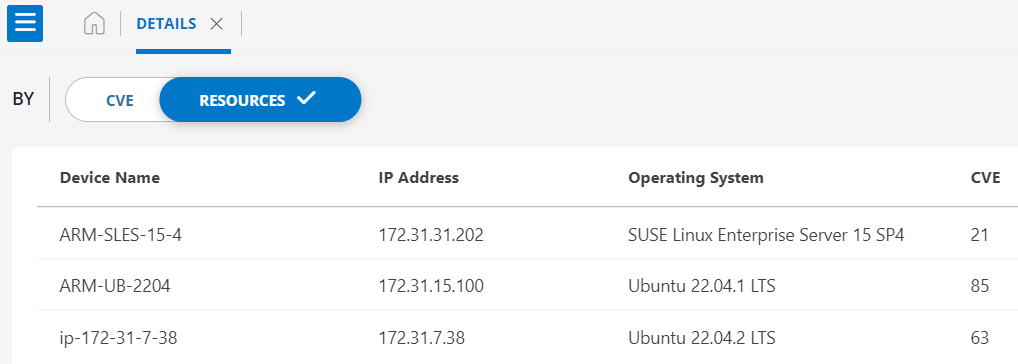
By clicking on any of the displayed Device Name above, you will be provided detailed information about the CVEs number for that specific device. Here is an example of what you can expect:
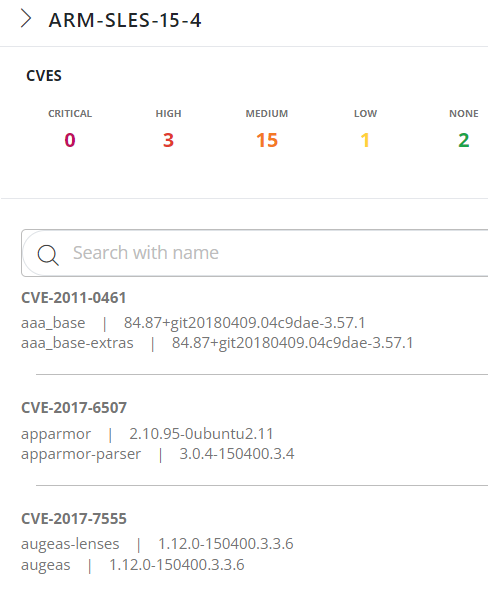
The following table describes the various information displayed on the Details page:
| Name | Description | |
|---|---|---|
| BY CVE | CVE ID | It is a unique, alphanumeric identifier assigned by the CVE Program. Each identifier references a specific vulnerability. |
| Severity | It shows the effect of severity on the operating system. | |
| Description | Detailed description mentioned for the CVE ID. | |
| Impacted OS | Listed of impacted OS. | |
| Impacted Resources | Show the number of resources impacted against each CVE. | |
| BY RESOURCES | Device Name | Name of the device. |
| IP Address | Show the IP Address of the devices. | |
| Operating System | Show the operating System for the devices. | |
| CVE | Show the number of Common Vulnerabilities and Exposures (CVE) against each device. |