Prerequisites
On Gateway
- OpsRamp Classic Gateway (Linux) version 15.0.0 or later.
- OpsRamp NextGen Gateway version 15.0.0 or later.
Note
We recommend using the latest Gateway version for full coverage of (Recent bug fixes, enhancements, etc.)- Ensure the cluster, standalone target, and all applicable nodes are accessible from the Gateway.
- Open TCP port 22 for PowerShell over SSH.
- For legacy PowerShell Remoting, open TCP ports 5985 and/or 5986.Note : By default, WS-Man and PowerShell remoting use port 5985 and 5986 for connections over HTTP and HTTPS, users should be present in nodes and cluster.
Non-Admin User Privileges
The following permissions are required regardless of the selected connection option:
- Configure the non-administrator user on the target cluster and all applicable nodes.
Note
Execute all commands in an elevated PowerShell session (Run as Administrator), unless Command Prompt is explicitly specified.1. Add User to the Performance Monitor Users Group
The user must be a member of the Performance Monitor Users group to collect performance counter metrics.
net localgroup "Performance Monitor Users" /add "<domain\user>"
2. Grant Remote WMI and Performance Monitor Access
Perform these steps on each monitored Windows system using an account with administrator rights.
- Press Windows Key + R, type
wmimgmt.msc, and press Enter. - In the left pane, right-click WMI Control (Local) and select Properties.
- Open the Security tab and expand Root.
- Select the namespace required by your monitoring product—such as CIMV2 or WMI—then click Security. These are different namespaces; do not treat them as interchangeable.
- Click Add, enter the non-administrator user account (for example,
DOMAIN\username), and click OK. - Select the account and allow:
- Enable Account
- Remote Enable
- Execute Methods and Read Security only if the product requires them.
- To apply the permissions to child namespaces, click Advanced, select the account, click Edit, and set Applies to to This namespace and subnamespaces.
- Click OK, then Apply, and close the WMI management windows.
Note
Execute Methods allows method execution, so the permissions are not strictly read-only if that permission is granted. Enable Account and Remote Enable are the core permissions for remote WMI access; follow the product’s requirements for any additional permissions.3. Grant Read-Only Failover Cluster Access
The domain user must be granted read-only access to the failover cluster.
Grant-ClusterAccess -User "<domain\user>" -ReadOnly
For monitoring services like Windows Cluster Service, Windows domain users must be a part of the Local Administrators group as the integration uses the Win32_Service class for fetching the details. Refer to Get-CimInstance.
Enable Windows Service Monitoring Permissions
If the non-administrator monitoring account cannot retrieve Windows service information because of insufficient permissions, follow these steps to grant service access without adding the account to the local Administrators group.
Note
Skip these steps if service monitoring already works with the existing account configuration. The example service permissions below include start and stop permissions, not just read/query access.- Retrieve the user SID of the user account from the monitored device.
- Open Command Prompt in Administrator mode.
- Run the following command to retrieve the user SID. Replace
UserNamewith the user name for the user account:
wmic useraccount where name="UserName" get name,sid
Example:
wmic useraccount where name="apiuser" get name,sid
- Note down the SID (for example,
S-1-0-10-200000-30000000000-4000000000-500). - Retrieve the current SDDL for the SC Manager.
- Run the following command to save the current SDDL for the SC Manager to
CurrentSDDL.txt:
sc sdshow clussvc > CurrentSDDL.txt
- Edit
CurrentSDDL.txtand copy the entire content. The SDDL will look like this:
D:(A;;CC;;;AU)(A;;CCLCRPRC;;;IU)(A;;CCLCRPRC;;;SU)(A;;CCLCRPWPRC;;;SY)(A;;KA;;;BA)(A;;CC;;;AC)S:(AU;FA;KA;;;WD)(AU;OIIOFA;GA;;;WD)
- Update the SDDL by creating a new snippet for the SID:
(A;;CCLCRPWPRC;;;<SID of User>)
Example:
(A;;CCLCRPWPRC;;;S-1-0-10-200000-30000000000-4000000000-500)
- Place this snippet before
S:in the original SDDL. The updated SDDL will look like this:
D:(A;;CC;;;AU)(A;;CCLCRPRC;;;IU)(A;;CCLCRPRC;;;SU)(A;;CCLCRPWPRC;;;SY)(A;;KA;;;BA)(A;;CC;;;AC)(A;;CCLCRPWPRC;;;S-1-0-10-200000-30000000000-4000000000-500)S:(AU;FA;KA;;;WD)(AU;OIIOFA;GA;;;WD)
- Execute the following command with the updated SDDL, replacing the example SID with the actual user SID:
sc sdset clussvc D:(A;;CC;;;AU)(A;;CCLCRPRC;;;IU)(A;;CCLCRPRC;;;SU)(A;;CCLCRPWPRC;;;SY)(A;;KA;;;BA)(A;;CC;;;AC)(A;;CCLCRPWPRC;;;S-1-0-10-200000-30000000000-4000000000-500)S:(AU;FA;KA;;;WD)(AU;OIIOFA;GA;;;WD)
Connection Modes
Starting from Windows Fail-over Cluster version 10.1.0, the option to select the connectionMode is available. The supported options are:
- PowerShell (existing)
- OpenSSH (new)
Note
PowerShell Remoting over WinRM is deprecated and will no longer be supported in the applicable updated application versions. These instructions apply only to earlier application versions that still support this connection option.PowerShell Remoting over WinRM
Configuration steps
- Enable PowerShell Remoting on every applicable target:
Enable-PSRemoting -Force
- Add the user to Remote Management Users:
net localgroup "Remote Management Users" /add "<user>"
- Add the OpsRamp Gateway IP to
TrustedHosts:
Set-Item WSMan:\localhost\Client\TrustedHosts -Force -Concatenate -Value "<OpsRampGatewayIP>"
To allow any host, when explicitly required:
Set-Item WSMan:\localhost\Client\TrustedHosts -Force -Value "*"
- Configure and restart WinRM:
    Set-Service WinRM -StartupType Automatic
    Restart-Service WinRM -Force
- Open WinRM ports on every applicable target:
- TCP 5985 for WinRM over HTTP.
- TCP 5986 for WinRM over HTTPS.
PowerShell pre-checks
Verify network connectivity from the Gateway:
ping <IP-address-or-hostname>
telnet <IP-address-or-hostname> 5985
telnet <IP-address-or-hostname> 5986
- For a Classic Gateway, launch PowerShell directly with
pwsh. - For a NextGen Gateway, enter the NativeBridge container and launch PowerShell:
    kubectl exec -it nextgen-gw-0 -c nativebridge -- /bin/bash
    pwsh
Test PowerShell Remoting using the integration credential:
$password = ConvertTo-SecureString -AsPlainText -Force -String "<password>"
$credential = New-Object `
        -TypeName System.Management.Automation.PSCredential `
        -ArgumentList "<username>", $password
$session = New-PSSession `
        -ComputerName "<IP-address-or-hostname>" `
        -Credential $credential `
        -Authentication Negotiate `
        -ErrorAction Stop
$session.State
The session state must be Open. Close the test session:
Remove-PSSession $session
A successful PowerShell session confirms connectivity and authentication only. The user must also have the application-specific permissions required to execute discovery and monitoring commands.
PowerShell over SSH using OpenSSH
If the user is non-administrator then must have the following privileges:
- Membership in the Performance Monitor Users group.
- Remote WMI read-only access to the Root\CIMV2 namespace and subnamespaces.
- Read-only access to the failover cluster.
The user should be added to all target nodes and the cluster:
- Create the same non-admin user account (local or domain) on all cluster nodes.
- Add the user to the
AllowUsersdirective insshd_configon each node. - Add the user to the local Hyper-V Administrators group on every node.
- Grant the user Read-Only permissions in the Failover Cluster configuration.
Pre-checks
Check whether OpenSSH Server is installed:
Get-WindowsCapability -Online -Name OpenSSH.Server*
Check the SSH service:
Get-Service sshd
Configuration steps
- Install OpenSSH Server if it is not already installed:
Add-WindowsCapability -Online -Name OpenSSH.Server~~~~0.0.1.0
- Start
sshdand configure automatic startup:
    Start-Service sshd
    Set-Service sshd -StartupType Automatic
- Open inbound TCP port 22:
    New-NetFirewallRule `
            -Name "Allow-SSH-Port-22" `
            -DisplayName "Allow SSH Port 22" `
            -Protocol TCP `
            -Direction Inbound `
            -LocalPort 22 `
            -Action Allow `
            -Profile Domain,Private,Public
- Open
C:\ProgramData\ssh\sshd_configas an administrator:
notepad C:\ProgramData\ssh\sshd_config
- Configure password authentication and the permitted user:
    PasswordAuthentication yes
    AllowUsers <ssh-username>
- Set Windows PowerShell as the OpenSSH default shell:
    Set-ItemProperty `
            -Path "HKLM:\SOFTWARE\OpenSSH" `
            -Name DefaultShell `
            -Value "$PSHOME\powershell.exe"
- Restart
sshdand confirm that it is running:
    Restart-Service sshd
    Get-Service sshd
Validate connectivity from the Gateway
ping <IP-address-or-hostname>
telnet <IP-address-or-hostname> 22
ssh <username>@<IP-address-or-hostname>
The SSH connection must be established successfully, and PowerShell must be configured as the default shell. After connecting, run the following command to verify the installed PowerShell version and confirm that the active shell is PowerShell:
$PSVersionTable.PSVersion
Configure Windows failover cluster monitoring
Click here to Configure and Install the Windows failover cluster monitoring Integration
- To select your client, navigate to All Clients, and click the Client/Partner dropdown menu.
Note: You may either type your client’s name in the search bar or select your client from the list. - Navigate to Setup > Account. The Account Details screen is displayed.
- Click Integrations. The Installed Integrations screen is displayed with all the installed applications.
Note: If you do not have any installed applications, you will be navigated to the Available Integrations and Apps page with all the available applications along with the newly created application with the version. - Click + ADD on the Installed Integrations page.
Note: Search for the integration either by entering the name of the integration in the search bar or by selecting the category of the integration from the All Categories dropdown list. - Click ADD in the Windows Fail-over Cluster application.
- In the Configuration screen, click + ADD. The Add Configuration screen appears.
- Enter the following BASIC INFORMATION:

| Field Name | Description | Field Type |
|---|---|---|
| Name | Enter the name for the configuration. | String |
| Windows Type | Select the type of Windows Server instance you are integrating:Available Options
| Dropdown |
| IP Address/Host Name | Enter the IP Address/Host Name of the Windows failover cluster monitoring. It should be accessible from Gateway. | String |
| Credentials | Select the credential associated with your Windows failover cluster monitoring account. If you want to use the existing credentials, select them from the Select Credentials dropdown. Else, click + Add to create credentials. The ADD CREDENTIAL window is displayed. Enter the following information.
| Dropdown |
| Connection Mode | Open SSH is the only supported option.Note: The PowerShell connection model was removed for security reasons. It is recommended to migrate to OpenSSH for continued support and enhanced compatibility.For more information, see Deprecation notice for PowerShell Communication. | Dropdown |
| App Failure Notifications | When selected, you will be notified in case of an application failure such as Connectivity Exception, Authentication Exception. | Checkbox |
| Connection TimeOut In Mins | Adds the feasibility to input nativebridge script execution time out in minutes. The default selection is 5 mins and the other available dropdown values are 10, 15, 20, 25, and 30. | Dropdown |
| Log File Monitoring | When selected (checked), log file monitoring is activated, allowing the system to track specific log files for changes, errors, or specific expressions. | Checkbox |
| Log File Configuration | Specifies the configuration details for the log file to be monitored. Default value:{"Name":"","Folder Path":"","File Name":"","Rotated Folder Path":"","Rotated File Name":"","Notify":[{"Monitor Type":"","Expression":"","Operator":"","Threshold":"","Severity":""}]} | String |
| Request Timeouts | Selecting this checkbox enables you to configure the timeout settings for NativeBridge connections and script execution requests made by the integration to the end device. | Checkbox |
| Connection Timeout In Mins | Select the maximum time, in minutes, that the integration should wait while establishing a connection with the nativeBridge. Default value: 10 minutes. | Dropdown |
| Connection Request Timeout In Mins | Select the maximum time, in minutes, required to process a NativeBridge HTTP call, from sending the request to receiving the response. Default value: 10 minutes. | Dropdown |
| Socket Timeout In Mins | Select the maximum allowable time of inactivity between two data packets during data exchange with the server. Default value: 10 minutes. | Dropdown |
| Script Execution TimeOut In Mins | Select the maximum execution time, in minutes, to be considered by the script. The default option is 5 minutes, with other available options being 10, 15, 20, 25, and 30 minutes. | Dropdown |
- CUSTOM ATTRIBUTES: Custom attributes are the user-defined data fields or properties that can be added to the preexisting attributes to configure the integration.
| Field Name | Description | Field Type |
|---|---|---|
| Custom Attribute | Select the custom attribute from the dropdown. You can add attributes by clicking the Add icon (+). | Dropdown |
| Value | Select the value from the dropdown. | Dropdown |
Note: The custom attribute that you add here will be assigned to all the resources that are created by the integration. You can add a maximum of five custom attributes (key and value pair).
- In the Native Types section, select the native types to be discovered.
- In the DISCOVERY SCHEDULE section, select recurrence pattern to add one of the following patterns:
- Minutes
- Hourly
- Daily
- Weekly
- Monthly
- Click ADD.
Windows type is available in two types - Standalone and Cluster.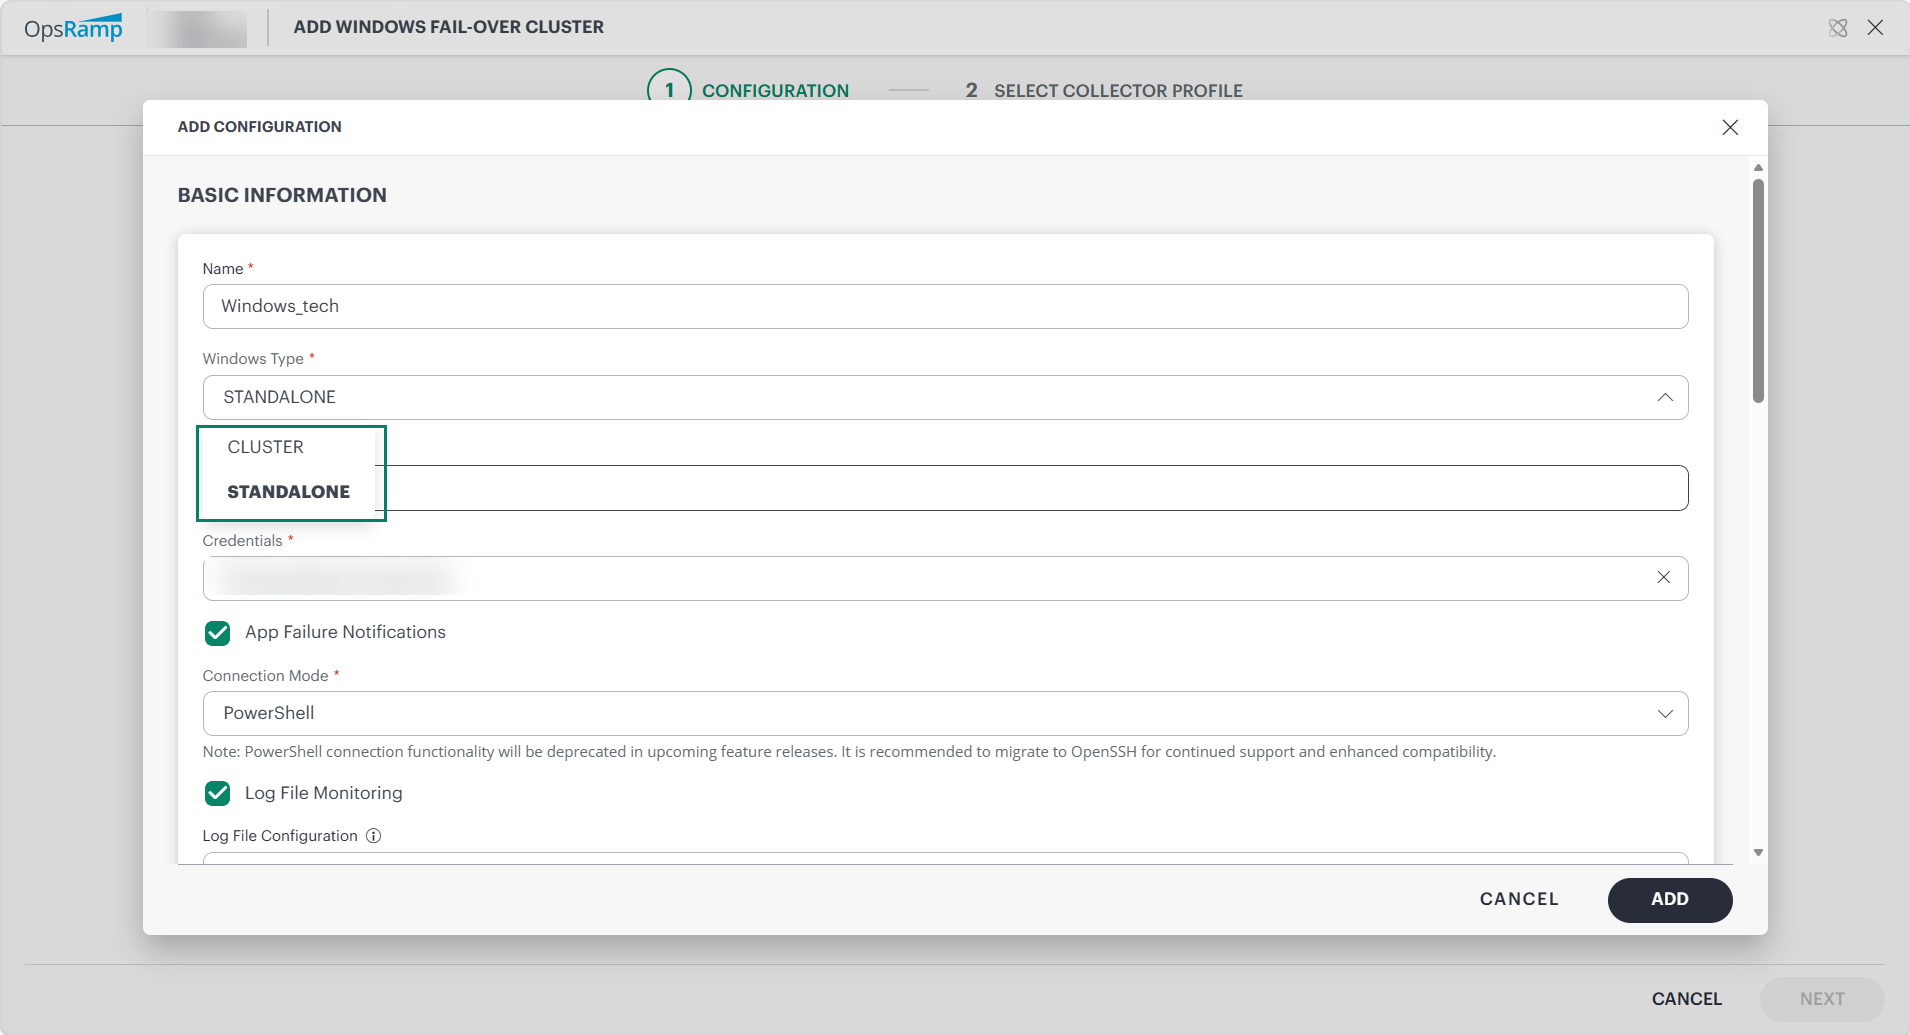
Connection Mode is available in two modes - Powershell and Open SSH.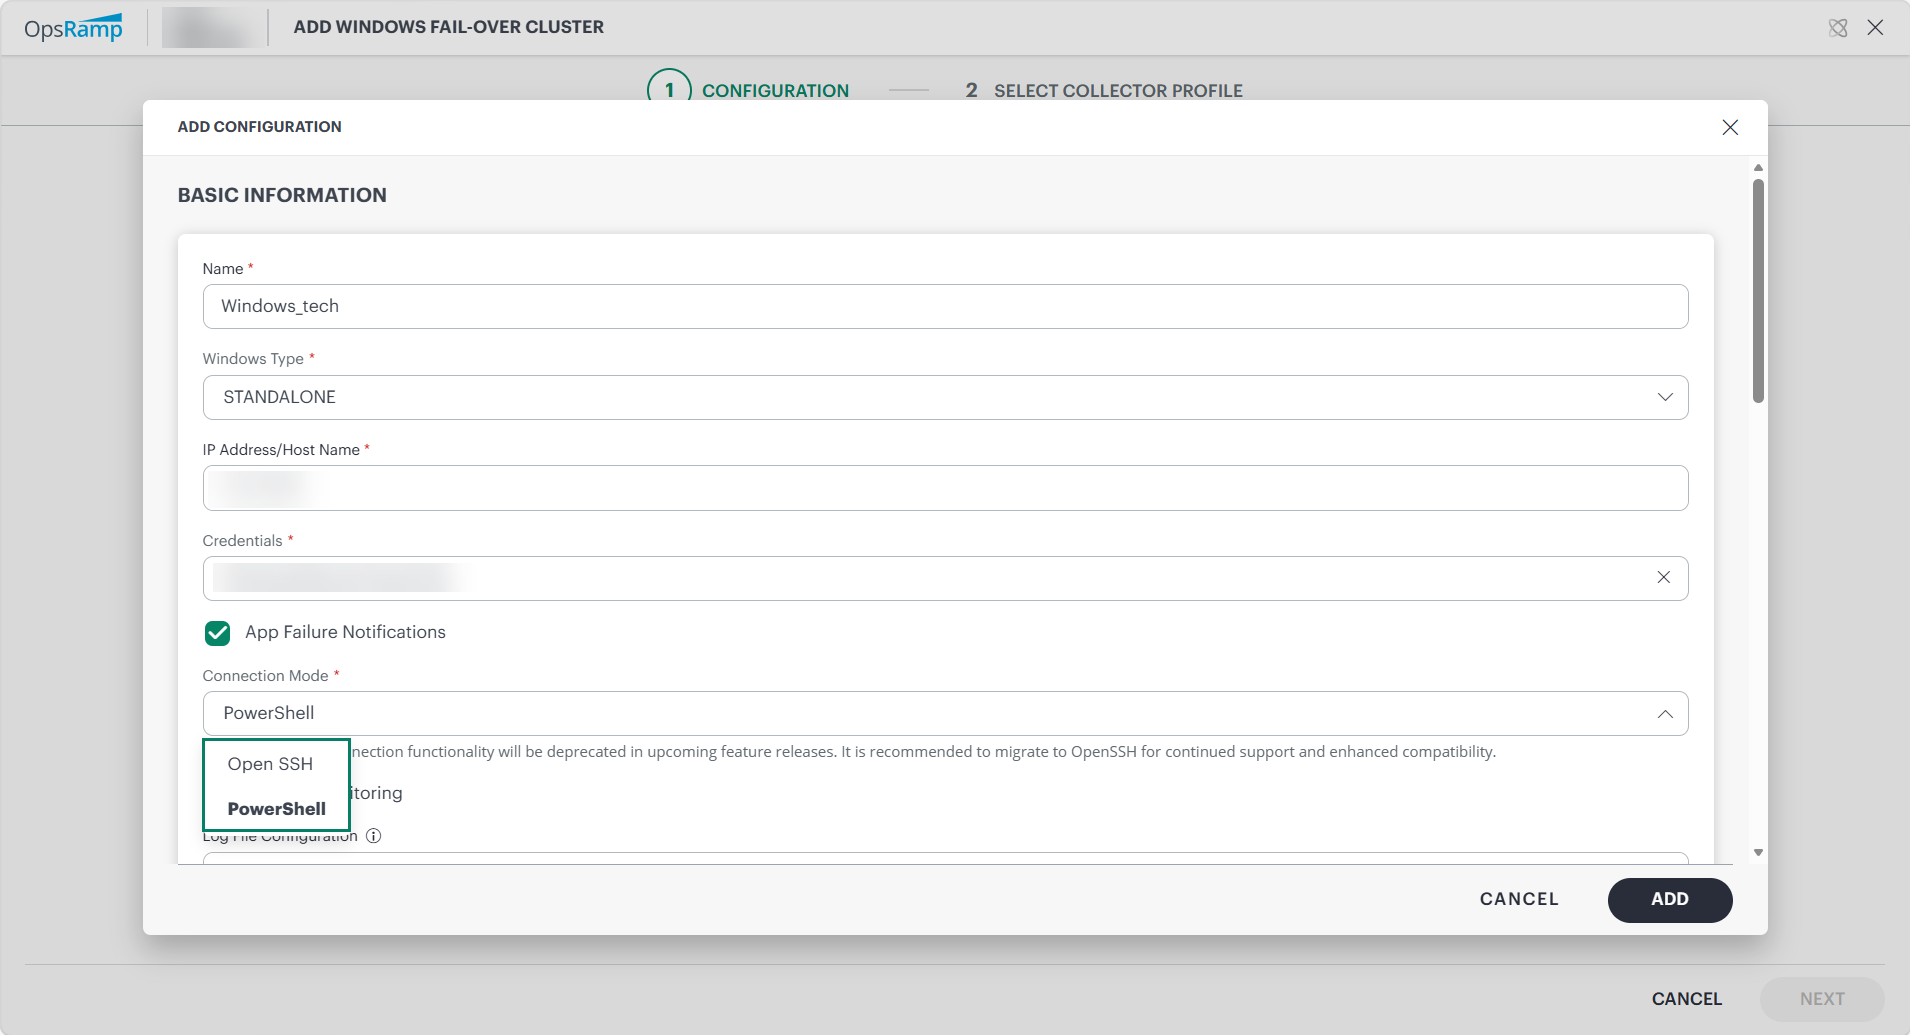
Now the configuration is saved and displayed on the configurations page after you save it.Note: From the same page, you may Edit and Remove the created configuration.
12. Under the ADVANCED SETTINGS, Select the Bypass Resource Reconciliation option, if you wish to bypass resource reconciliation when encountering the same resources discovered by multiple applications.
Note: If two different applications provide identical discovery attributes, two separate resources will be generated with those respective attributes from the individual discoveries.
13. Click NEXT.
14. (Optional) Click +ADD to create a new collector. You can either use the pre-populated name or give the name to your collector.
15. Select an existing registered profile.
- Click FINISH.
The integration is installed and displayed on the INSTALLED INTEGRATION page. Use the search field to find the installed integration.
Modify Windows failover cluster
Click here to Modify the Configuration
See Modify an Installed Integration or Application article.
Note: Select Windows failover cluster.
Discover Resources in Windows failover cluster
Click here to View the Windows failover cluster Details
The discovered resource(s) are displayed in the Infrastructure page under Infrastructure > Search > OS-High Availability > Windows Fail-over Cluster, with Native Resource Type as Windows Failover Cluster. You can navigate to the Attributes tab to view the discovery details, and Metrics tab to view the metric details for Windows Failover Cluster.
The cluster nodes are displayed under Components.